Tap-to-Pay on Your Phone: How It Works, Where It’s Safe, and When It Can Fail
Your phone can act like a credit card at checkout. Learn what “tap-to-pay” really does, what cashiers can’t see, and the simple habits that make it safer.
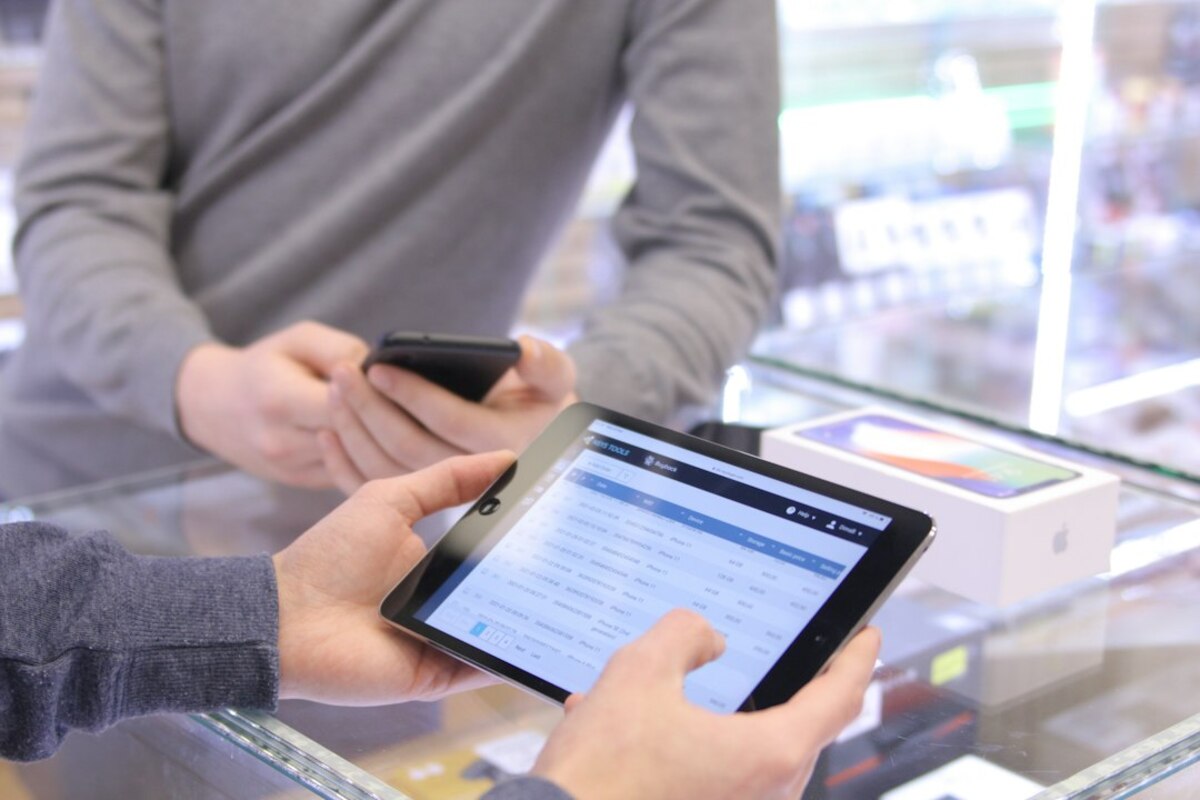
- Tap-to-pay usually sends a one-time code, not your real card number, which helps limit damage if data is stolen.
- It’s typically safer than swiping a magnetic stripe—and often safer than handing over your physical card.
- Most tap failures are boring (case, settings, terminal), and a few quick checks fix them fast.
What “tap-to-pay” actually means (and what it’s not)
You’ve probably seen it at a grocery store, café, or pharmacy: a little symbol that looks like a sideways Wi‑Fi icon on the payment terminal. You hold your phone near the reader, it buzzes, and you’re done. It feels like magic—until you wonder: did I just broadcast my card details through the air?
Tap-to-pay on a phone (Apple Pay, Google Wallet, Samsung Wallet, and similar services) uses a technology called NFC (Near Field Communication). “Near field” is the key phrase: it works only at very short range—typically a few centimeters. Think of it like a whisper that only the checkout terminal can hear when your phone is very close. It’s not like Bluetooth, where devices chat from across the room.
It also isn’t the same as paying with a QR code (where you scan a code on-screen) or paying online (where you type in card numbers). Tap-to-pay is designed for in-person terminals and leans heavily on the security features already built into modern phones.
A simple way to picture it:
- Swiping a card is like giving a cashier a photocopy of your card’s “identity.”
- Inserting a chip card is like your card proving it’s real by doing a quick cryptographic handshake.
- Tapping your phone is like sending a single-use “payment ticket” that works for that purchase only.
That single-use idea is the heart of why tap-to-pay is often considered safer than older methods.
The invisible safety features: tokens, one-time codes, and your lock screen
When you add a card to your phone’s wallet app, the phone usually does not store and transmit your actual card number at the register. Instead, it uses a concept called tokenization.
Tokenization means your bank (and the payment network like Visa/Mastercard) creates a “stand-in” number for your card. That stand-in is called a token. The token is tied to:
- your specific card,
- your specific phone (or watch), and
- the wallet service that manages it.
At checkout, your phone sends the token plus a one-time cryptographic code (often called a dynamic security code or cryptogram). This code changes every time. So even if someone captured the signal (hard to do at that distance and with encryption), it wouldn’t be reusable for a second purchase.
There’s also a second layer most people forget: device authentication. Your phone typically requires Face ID, fingerprint, PIN, or passcode before it will pay—especially for larger amounts. That means a lost phone is not the same as a lost card. A lost card can be tapped by whoever finds it (until you freeze it). A locked phone can’t usually pay without your face or finger.
To make the differences clearer, here’s a quick comparison.
| Payment method | What you hand over | What can be copied easily? | Typical weak spot |
|---|---|---|---|
| Magnetic stripe swipe | Static card data (same every time) | High | Skimmers, copied stripe data |
| Chip insert | Card performs a secure transaction | Low | PIN entry shoulder-surfing, social engineering |
| Contactless card tap | Contactless transaction with dynamic data | Low | Lost/stolen card used for small taps |
| Phone tap-to-pay | Token + one-time code (and device confirmation) | Very low | Unlocked phone, weak screen lock, account takeover |
What the cashier can see: usually the same things they’d see with any card—your name (sometimes), last four digits, and whether it went through. They generally can’t see your full card number, and they definitely can’t “download” your card just because you tapped.
What the store gets: the info needed to process the payment. Tokenization is specifically meant to reduce the value of stolen payment data in store breaches.
If you’ve ever heard the phrase “digital wallet,” this is why it’s more than a fancy app. It’s a different way to represent your card at the moment of payment.
Real-life moments: when tap-to-pay shines, and when it trips you up
Tap-to-pay is popular because it saves time and reduces friction. But it also changes small day-to-day behaviors in ways you notice.
Scenario: the coffee rush. You’re holding a bag, your phone is already in your hand, and the line is moving fast. Tapping your phone can be quicker than digging out a wallet, inserting a card, waiting, and putting it back. This is one reason transit systems and quick-service shops pushed contactless so hard.
Scenario: the “I don’t want to hand over my card” moment. At busy counters, cards sometimes sit on top of terminals, get swapped by mistake, or simply end up out of your sight. With tap-to-pay, your phone stays with you, and you approve the payment on your screen.
Scenario: your card gets replaced. If your bank reissues your card, some wallet services can update in the background. That means fewer “why is my card declined?” surprises—though not every bank handles this smoothly.
Now for the annoyances—because everyone hits them eventually:
- The phone doesn’t tap: Often it’s a thick case, a metal wallet insert, or you’re tapping the wrong spot. Many phones have the NFC antenna near the top or middle-back; moving the phone slightly can fix it.
- The terminal is contactless… but disabled: Some stores have the symbol yet have contactless turned off (policy, old contracts, or a broken reader). If it won’t respond after a couple tries, it may not be you.
- You hit a limit: Some regions/merchants set limits for contactless transactions. Your phone may handle higher amounts than a contactless card because it uses biometric confirmation, but limits can still exist.
- Battery anxiety: If your phone dies, your wallet dies with it. (Some phones support a small “reserve” power mode for transit or a few taps, but you shouldn’t rely on it.)
If you want a quick “fix-it” checklist, try this order:
- Wake the phone and authenticate (Face ID/fingerprint/PIN).
- Remove the phone from a thick or metal case (or move it away from magnets/pop-sockets temporarily).
- Hold steady for 1–2 seconds right where the reader indicates (don’t wave it like a wand).
- Try a different angle (top edge vs. center-back).
- If it still fails, use chip insert (most reliable fallback) or another card.
Common worries: “Can someone steal my money just by standing near me?”
This is the question that keeps tap-to-pay in the “sounds cool, but…” category for many people. The short version is: drive-by theft is difficult and unlikely with phone tap-to-pay, and the system is designed to make stolen radio data useless.
Here’s what would generally need to go wrong for a stranger to get a fraudulent payment out of your phone:
- Your phone would have to allow payments without authentication (uncommon for phones, more relevant for some contactless cards).
- The attacker would have to get your phone extremely close to a payment terminal or a specialized reader without you noticing.
- Even then, the phone’s token + one-time code approach limits reuse.
More realistic risks are the boring, modern ones:
- Account takeover: If someone gains access to your Apple/Google account and your device, they might attempt wallet changes.
- Stolen unlocked phone: If your phone is stolen while unlocked (or your passcode is easily guessed), the thief may be able to use it before you lock it down.
- Phishing texts and fake support calls: Criminals increasingly target people, not NFC signals—trying to trick you into approving a login or sharing a one-time code.
Practical habits that make a big difference:
- Use a strong passcode (not 0000, 123456, or your birthday).
- Turn on biometric unlock and require it for wallet payments.
- Enable “Find My” / device locator so you can lock or erase a lost phone quickly.
- Keep notifications sensible: payment notifications can help you spot fraud fast, but lock-screen previews can reveal info if your phone is unattended.
Often, no. Many tap-to-pay transactions can work offline because the phone can generate the needed one-time codes without a live connection. But some situations (first-time setup, certain security checks, or wallet updates) may require internet.
Often, no. Many tap-to-pay transactions can work offline because the phone can generate the needed one-time codes without a live connection. But some situations (first-time setup, certain security checks, or wallet updates) may require internet.
In many everyday cases, yes—especially compared to swiping a magnetic stripe. Phone payments typically use tokenization plus device authentication, which reduces the value of stolen data and makes “found phone” fraud harder than “found card” fraud.
In many everyday cases, yes—especially compared to swiping a magnetic stripe. Phone payments typically use tokenization plus device authentication, which reduces the value of stolen data and makes “found phone” fraud harder than “found card” fraud.
Common reasons include NFC being turned off (on some devices), needing to unlock/authenticate first, a thick or metal case interfering, or simply tapping the wrong area of the phone. Card antennas are often easier to align because they’re standardized.
Common reasons include NFC being turned off (on some devices), needing to unlock/authenticate first, a thick or metal case interfering, or simply tapping the wrong area of the phone. Card antennas are often easier to align because they’re standardized.
If you’re deciding whether to try tap-to-pay, a good low-stress approach is to add one card, use it in a familiar store, and keep your physical card as backup for the first week. Once you’ve done a few normal transactions—groceries, coffee, pharmacy—it stops feeling like a trick and starts feeling like a shortcut you always had.
One last detail that surprises people: tap-to-pay can also work on smartwatches. That’s handy when your hands are full (stroller, luggage, or just carrying too much), but it’s also a reminder: treat wearable devices like wallets. Use a passcode on the watch and enable the feature that requires re-authentication when you take it off.